AttackIQ Names Former DISA CTO Dave Mihelcic Field CTO – Federal
Veteran federal technology leader will help government agencies operationalize proactive, AI-powered cyber defense and
Press Release Disclaimer: This is a press release distributed through the XPR Media network. It has not been independently verified by our newsroom.


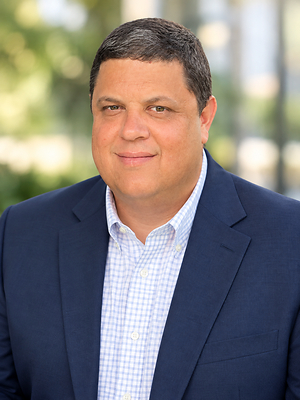
AttackIQ, the leader in threat-informed Continuous Threat Exposure Management (CTEM), today announced the appointment of Dave Mihelcic as Field Chief Technology Officer – Federal. A former Chief Technology Officer of the Defense Information Systems Agency (DISA), Mihelcic will help federal agencies modernize cyber defense operations by adopting proactive, threat-informed, and AI-powered capabilities that continuously validate defensive effectiveness and improve mission readiness.
In his new role, Mihelcic will work directly with federal technology and cyber leaders to translate mission requirements into operational CTEM programs. He will help Federal agencies move beyond periodic assessments, compliance-driven exercises, and reactive security processes toward a continuous operating model that uses current threat intelligence, adversary emulation, and evidence-based validation to identify defensive gaps, optimize controls, and measurably reduce threat debt.
Mihelcic will also guide Federal adoption of AttackIQ’s AVA Agentic OS, the agentic operating system purpose-built for CTEM. AVA orchestrates specialized AI agents across cyber threat intelligence, adversary exposure validation, detection engineering, control optimization, attack-path reduction, and AI security validation. By transforming fragmented and labor-intensive security activities into coordinated cyber missions, AVA enables federal cyber teams to operate with greater speed, scale, and precision while keeping human experts in command of priorities and mission decisions.
“Dave understands better than almost anyone what it takes to design, deploy, and sustain technology for the federal government’s most consequential missions,” said Carl Wright, Chief Commercial Officer at AttackIQ. “His experience as DISA’s CTO, combined with his deep understanding of the operational realities facing Federal cyber teams, will be invaluable as agencies shift from reactive security and periodic compliance to continuous, AI-enabled cyber defense. Dave will help our customers turn CTEM into an operational capability, and he will bring the leadership and accountability required to ensure the DISA AEV program delivers measurable mission success across the Department of War.”
As Field CTO – Federal, Mihelcic will also be responsible for program management of the AttackIQ DISA enterprise Adversarial Exposure Validation (AEV) program. DISA selected AttackIQ as the enterprise AEV platform for deployment across the Department of War, establishing a common capability for continuously assessing defenses against real-world adversary behavior and providing enterprise visibility into cyber readiness.
Mihelcic will coordinate closely with DISA, Defense Agencies, Military Services, Combatant Commands, mission partners, and AttackIQ teams to drive deployment, adoption, workforce enablement, operational consistency, and measurable mission outcomes. His responsibilities will include aligning implementation with mission priorities, establishing a repeatable operating model across participating organizations, accelerating the effective use of AVA Agentic OS and AttackIQ’s validation capabilities, and ensuring leaders receive actionable evidence about defensive performance.
He will also help integrate technology, process, training, and governance so the program creates an enduring operational capability across joint, coalition, and distributed environments.
“Federal agencies are facing adversaries that are using automation and artificial intelligence to operate faster and at greater scale, and our defensive model must evolve accordingly,” said Dave Mihelcic, Field CTO – Federal at AttackIQ. “AttackIQ gives cyber leaders the ability to continuously test what matters, understand whether their defenses will perform against relevant adversary behaviors, and use evidence to focus resources where they will have the greatest mission impact. I am excited to help Federal agencies operationalize this proactive approach and to work with DISA and the Department to ensure the enterprise AEV program delivers lasting and significant improvements in cyber readiness.”
Mihelcic brings deep experience leading technology strategy and execution inside one of the federal government’s most complex mission environments. He spent 18 years at DISA and served as its CTO for more than 12 years. In that role, he was the Agency’s senior authority on scientific, technical, and engineering matters and was responsible for technology supporting DISA’s mission as the primary information technology and cybersecurity provider for the Department of War.
Mihelcic also led a diverse technical workforce of more than 900 engineers and scientists and represented the agency on engineering matters with Combatant Commands, Military Services, Defense Agencies, the Intelligence Community, and industry.
His appointment reinforces AttackIQ’s commitment to helping federal agencies establish a common, threat-informed operating model for cyber defense—one that continuously validates controls, improves detection coverage, breaks attack paths, reduces threat debt, and provides leaders with measurable evidence of mission readiness.
About AttackIQ
AttackIQ is the leader in threat-informed Continuous Threat Exposure Management, helping organizations continuously validate defenses, break attack paths, and reduce threat debt through evidence-based security operations.
Through AVA Agentic OS, AttackIQ has introduced the industry’s first agentic operating system purpose-built for CTEM, enabling organizations to execute Continuous Threat Exposure Management autonomously at enterprise scale. By orchestrating specialized AI agents across threat intelligence, adversary exposure validation, security validation, detection engineering, control optimization, threat debt reduction, and AI security validation, AttackIQ transforms fragmented security activities into continuous cyber resilience.
Trusted by the world’s largest enterprises, government agencies, and managed security providers, AttackIQ empowers organizations to continuously discover, validate, and reduce cyber risk with confidence.
CTEM Runs on AVA.
View source version on businesswire.com: https://www.businesswire.com/news/home/20260922282725/en/
Media gallery